XaasIO Solutions · Air-gapped

A Full-Stack Air-Gapped Cloud With AI for Critical Infrastructure

Defense, energy, utilities, transport and other critical infrastructure operators run the complete XaasIO stack inside an isolated boundary: private cloud, Kubernetes, storage, databases, security monitoring and response, disaster recovery and secure collaboration, with local identity, local registries and updates that arrive only as signed, scanned and approved offline bundles. AI runs inside the same fence: open-weight models served by the XaasIO AI Token Factory from a local model store and grounded in private data through the XaasIO AI Lake, with no public model or API in the request path.
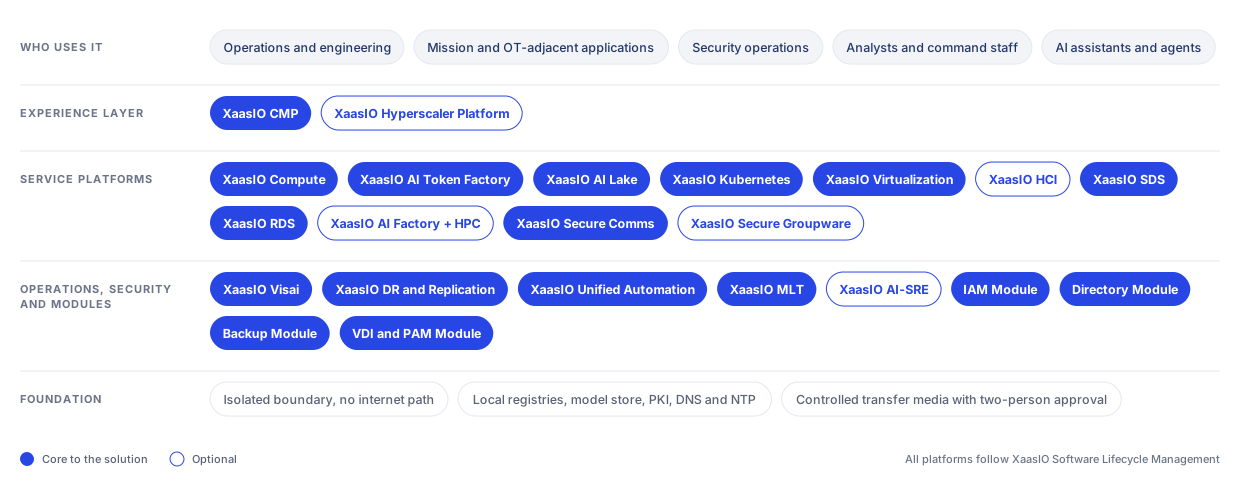
Built on XaasIO Compute, Virtualization, HCI, Kubernetes, SDS, RDS, CMP, AI Token Factory, AI Lake, AI Factory + HPC, Visai, DR and Replication, Unified Automation, Secure Communication and Collaboration, and Secure Groupware, and operated with MLT and AI-SRE, with all four modules. No public dependency in the request path.
Why now

What Gets in the Way

Cloud tooling assumes the internet

Registries, identity providers, update feeds, licensing servers and AI APIs all expect a connection the site does not have.

Air gaps erode

Ad-hoc USB updates and vendor laptops become the way things get done, and the boundary stops meaning anything.

AI pressure inside the fence

Operators want assistants, analytics and automation on sensitive data that must never leave the site, and a public model API is not an option.

Use cases

What You Can Deliver

Mission and operations cloud

Virtual machines, Kubernetes, storage and databases for mission applications and operational systems, with identity and policy inside the boundary.

Air-gapped AI inference

Open-weight models served from a local model store by the XaasIO AI Token Factory as OpenAI-compatible APIs, with local metering and audit and no public model in the request path.

Private data as AI context

The XaasIO AI Lake inside the boundary: lakehouse tables, a vector database and a knowledge graph over operational, document and telemetry data, so assistants, RAG and agents answer from your data only.

Security monitoring and governed response

Threat detection and human-governed response orchestration with XaasIO Visai, on logs and telemetry that never leave the site.

Resilience across sites

Replication and recovery between isolated sites over controlled links, with tested failover and failback.

Secure communication

Messaging, voice, video, mail and calendars for staff, self-hosted on the same stack.

How XaasIO delivers it

Everything inside the boundary

Compute, Virtualization or HCI, Kubernetes, SDS, RDS and the CMP console, with local identity, directory, PKI, DNS, NTP, image and chart registries and documentation.

Technical reference: XaasIO Compute · Virtualization · HCI · Kubernetes · SDS · RDS · CMP · IAM and Directory Modules

Air-gapped AI inference on open-weight models

The AI Token Factory air-gapped build serves open-weight models from a local model store, with tokenizers and licenses inside the fence, OpenAI-compatible APIs, per-team quotas, local metering and audit. There is no hybrid gateway, so nothing can fall back to a public model. The AI Factory + HPC build adds fine-tuning on site when training GPUs are available.

Technical reference: XaasIO AI Token Factory · vLLM · Open-weight families such as Llama, Mistral, Qwen and Gemma · XaasIO AI Factory + HPC

Private data as governed context

The AI Lake air-gapped build ingests documents, operational records and telemetry into Iceberg tables, embeds them into the vector database and links them in the knowledge graph under access policy and lineage. Retrieval, prompts and answers stay inside the fence, and every retrieval and token is logged.

Technical reference: XaasIO AI Lake · Context Lake and Agent Lake · Trino and Spark · Qdrant or pgvector

Security and response

Visai monitoring, threat detection and human-governed response; logging and telemetry in XaasIO MLT; privileged access management for administrators.

Technical reference: XaasIO Visai · XaasIO MLT · VDI and PAM Module

Signed offline updates

A controlled external staging environment acquires, scans and signs bundles, model weights and licenses included; controlled media carries them across; the site verifies, imports and records every update.

Technical reference: XaasIO Unified Automation Platform · SBOM · Signed artifacts

Resilience and recovery

Backup policy and restore management, replication and recovery plans between sites, and drills with evidence for audits.

Technical reference: Backup Module · XaasIO DR and Replication

Built on the XaasIO lineup

The Platforms and Modules Behind This Solution

Every platform and module below is part of XaasIO Software Lifecycle Management, the framework that gives all 20 platforms and 4 modules one release cycle, signed artifacts and an SBOM per release.

Platform or module Lifecycle scope Layer
XaasIO CMP PlatformCore Unified inventory, policy, approvals and infrastructure automation Experience layer
XaasIO Hyperscaler PlatformOptional Self-service cloud delivery, tenant services, metering and billing Experience layer
XaasIO Compute PlatformCore Private-cloud compute, networking and infrastructure orchestration Service platform
XaasIO AI Token FactoryCore Governed and metered AI inference services Service platform
XaasIO AI Lake PlatformCore Governed data, lakehouse and enterprise-context foundations Service platform
XaasIO Kubernetes PlatformCore Container orchestration and Kubernetes cluster lifecycle management Service platform
XaasIO Virtualization PlatformCore Virtual-machine, host and cluster lifecycle management Service platform
XaasIO HCI PlatformOptional Integrated compute, storage and networking with coordinated cluster lifecycle Service platform
XaasIO SDS PlatformCore Software-defined block, object and file storage Service platform
XaasIO RDS PlatformCore Database provisioning and management on Kubernetes Service platform
XaasIO AI Factory + HPC PlatformOptional Accelerated AI, scientific computing and high-performance workloads Service platform
XaasIO Secure Communication and Collaboration PlatformCore Self-hosted secure messaging, voice and video conferencing Service platform
XaasIO Secure Groupware PlatformOptional Self-hosted webmail, shared calendars and address books Service platform
XaasIO Autonomous Defense Platform (Visai)Core Human-governed security monitoring, threat detection and response orchestration Operations, security and modules
XaasIO DR and Replication PlatformCore Replication, recovery orchestration and recovery planning Operations, security and modules
XaasIO Unified Automation PlatformCore GitOps delivery, event-driven automation, configuration management, image builds and infrastructure as code Operations, security and modules
XaasIO MLT PlatformCore Operational visibility across platform health, logs and telemetry Operations, security and modules
XaasIO AI-SRE PlatformOptional AI-assisted incident analysis, recommendations and human-governed remediation Operations, security and modules
XaasIO IAM ModuleCore Identity, authentication and access-management integration Operations, security and modules
XaasIO Directory Services ModuleCore Centralized directory, user and group management Operations, security and modules
XaasIO Backup ModuleCore Backup policy, scheduling, retention and restore management Operations, security and modules
XaasIO VDI and PAM ModuleCore Virtual desktop lifecycle and governed privileged access Operations, security and modules

Core platforms are part of every deployment of this solution; optional ones are added when the estate needs them. Platforms without a page of their own yet link to the lifecycle framework.

Before and after

What Changes

Today With XaasIO
Public registries and identity providers Local registries, PKI and identity inside the boundary
Ad-hoc media and vendor laptops Signed offline bundles with two-person approval
No AI, or AI through a public API Open-weight models served inside the fence, no public fallback
Documents and telemetry nobody can query AI Lake context on site: lakehouse, vector database and knowledge graph
Security tooling that phones home Visai monitoring and response on local data
Backups without recovery evidence Replication, drills and audit evidence
Unsupported components inside the fence One release cycle with an SBOM per platform
Who it is for

Built for Organizations Like These

Defense and national security

Classified and isolated networks that need a supported cloud and AI platform without any external path.

Energy, utilities and transport

Operators with OT-adjacent environments, regulatory isolation requirements and long asset lifecycles.

Critical manufacturing and research

Sites that protect process data and intellectual property by design and still need modern platforms.
How to start

From Assessment to Operations

01

2 to 4 weeks

Boundary blueprint

Scope, security architecture, update process, identity, sizing, the model and data policy, and the list of platforms inside the fence.

02

2 to 4 weeks

Staging and first bundle

The external staging environment, the signed bundle procedure and the first verified import, models and licenses included.

03

6 to 12 weeks

Site build

Platforms deployed from the bundle: cloud, Kubernetes, storage, databases, the model store and AI Lake, security, DR and collaboration.

04

Ongoing

Operate

Local operations by your team with XaasIO support, or a cleared XaasIO SRE Pod on site, with scheduled update cycles.

Durations are typical for a mid-sized estate and are confirmed in the assessment. Every phase ends with a written deliverable and a decision point.
Why XaasIO

One Vendor for the Whole Stack, One Lifecycle for All of It

Validated as One Architecture

The platforms in this solution are tested together, not assembled on site, so the integration burden stays with XaasIO.

Controlled Lifecycle

Every platform and module follows XaasIO Software Lifecycle Management:a release identity, documented patching and upgrade paths, compatibility and rollback procedures.

Software Supply Chain Assurance

Upstream and XaasIO release SBOMs, signed artifacts, license and vulnerability review and SPDX or CycloneDX outputs for audit evidence.

Flexible Operating Model

Customer-operated with XaasIO support, co-managed, fully managed or a dedicated XaasIO SRE Pod, with 16×5 or 24×7 coverage.

Frequently asked questions


What does “no public dependency” mean in practice?
No registry, identity provider, update feed, license server, telemetry endpoint or model API outside the boundary is in the request path. Everything the platforms need runs inside, and updates arrive only as signed offline bundles.
How do updates get in?
Through a controlled external staging environment that acquires packages, images, models and advisories, scans them, produces SBOM and license reviews and signs a versioned bundle. Controlled media with two-person approval carries it across; the site verifies the signature, scans again and imports it, with rollback media kept.
Can AI really run without the internet?
Yes. Open-weight models, tokenizers and licenses arrive in the signed bundle and live in the local model store, with license review recorded. The AI Token Factory serves them as OpenAI-compatible APIs with local metering and audit, and the hybrid gateway is absent, so nothing can fall back to a public model. The AI Factory + HPC build fine-tunes models on site when training GPUs are available.
How does an assistant answer from our data without the data leaving?
Through the AI Lake inside the boundary. Documents, operational records and telemetry are ingested into lakehouse tables, embedded into the vector database and linked in the knowledge graph under access policy. Retrieval runs locally, the prompt and the answer stay inside the fence, and every retrieval and token is logged for audit.
How is security monitored?
XaasIO Visai provides monitoring, threat detection and human-governed response orchestration on logs and telemetry collected by XaasIO MLT inside the boundary. Administrator access goes through the VDI and PAM Module.
What about support if XaasIO cannot connect?
Support works through cleared staff, documentation inside the boundary and scheduled on-site or escorted sessions. Metrics XaasIO reports for the site are update lead time, signature verification, audit completeness, backup and restore success and catalog currency.
Is the whole stack certified for our regime?
The platforms are architected to align with the control families your regime requires, and the SBOMs, signed artifacts and documented procedures provide the evidence. Formal certification status is confirmed per deployment.

OpenStack, KVM, Ceph, Kubernetes, vLLM, Llama, Mistral, Qwen, Gemma, Apache Iceberg, Trino, Apache Spark, Qdrant, Matrix, Jitsi, SOGo, NVIDIA, and other product names are trademarks of their respective owners and are named for identification only. XaasIO is not affiliated with, endorsed by, or sponsored by these organizations.

Build what the world depends on.

Planning a cloud for government, financial services, pharmaceuticals, healthcare, energy, transport, industry, service-provider operations, or private AI? Work with XaasIO to define the architecture, security boundary, and operating model your environment requires.